 By carl
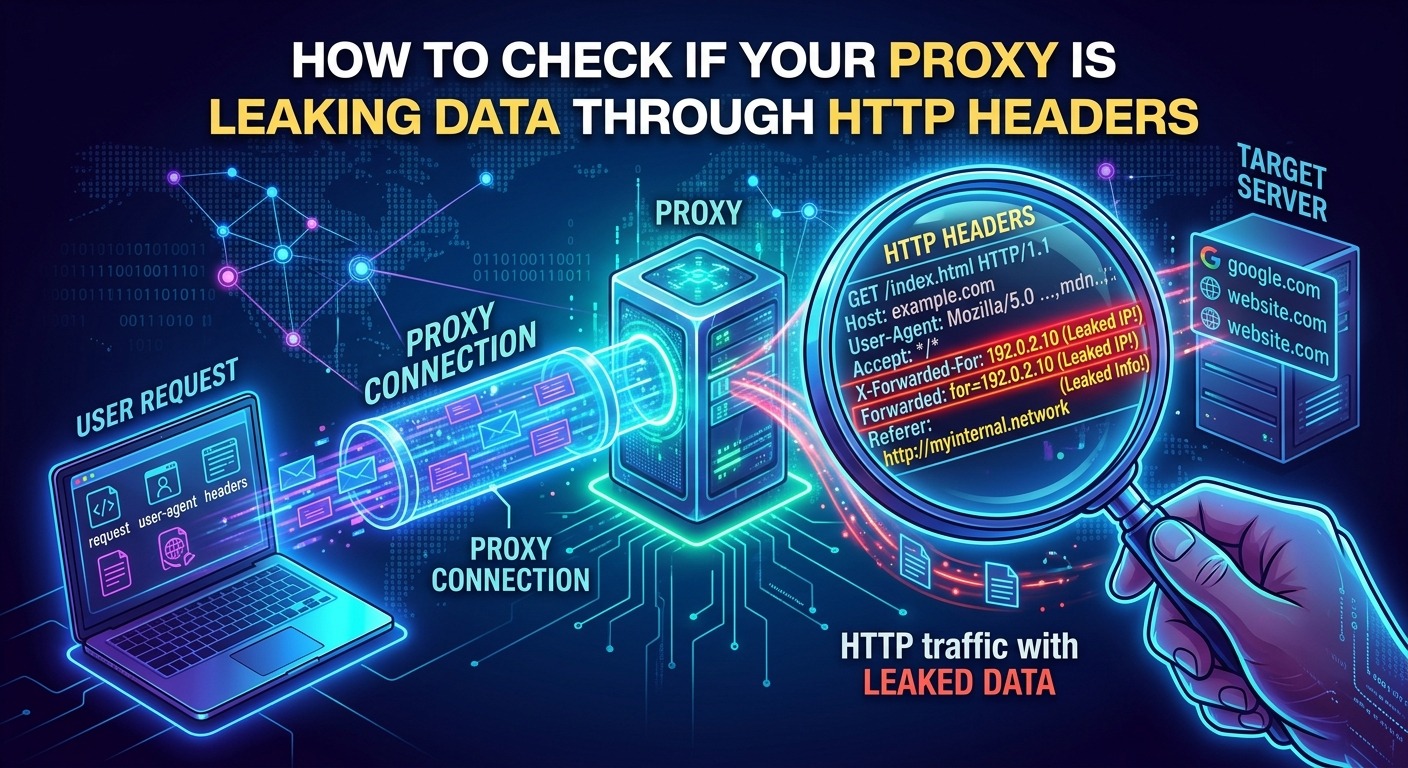
You set up a proxy, point your browser through it, and head to a “what is my IP” site. A different IP stares back at you. Done, right? Not quite. While your visible IP address has changed, a web server on the other end may already be reading something else entirely. Tucked inside the HTTP request headers, your original IP address could still be traveling alongside every page you visit. The proxy changed the messenger but forgot to check the message it was carrying.
Switching your IP is not the same as hiding your identity. Many proxies, especially free or poorly configured ones, pass along HTTP headers like X-Forwarded-For and Via that expose your original IP to every server you contact. Knowing how to read those headers on your own connection gives you hard evidence of whether your proxy is actually protecting you or just creating the illusion of privacy.
Why Changing Your IP Address Is Only Half the Story
Most people test a proxy by checking their visible IP. That makes sense because the IP address is the most obvious identifier. But HTTP traffic carries a lot more than just a source address. When a request passes through an intermediary server, that server often adds metadata about where the request originally came from. This metadata travels forward to the destination site.
A website does not need to do deep packet inspection to read this. The information sits right at the top of every request, plain as day, in the HTTP headers. Any backend developer can log it in seconds. Any analytics platform can capture it automatically. Your anonymity depends not just on what IP shows up in the connection, but on what the proxy puts inside the request itself.
The Three Headers That Give You Away
Three headers are responsible for most proxy-related leaks. Understanding each one helps you know exactly what to look for during a diagnostic check.
The X-Forwarded-For header is the most well-known culprit. It was designed to help load balancers and reverse proxies log the original client IP. The format is simple: the header lists IP addresses in a chain, with the original client IP listed first. A transparent proxy that adds this header without stripping your real IP is handing it directly to any web server that checks.
The Via header is older and defined in the HTTP specification itself. It identifies which proxy servers handled a request, including version information. Even if X-Forwarded-For looks clean, a Via header can confirm that a proxy was involved and give clues about its configuration. The standardized behavior of forwarding headers, including a formal replacement for X-Forwarded-For, is documented in RFC 7239, the internet standard that brought structure to how proxies should identify themselves.
The X-Real-IP header is less common but follows the same logic. Some proxy software uses it instead of X-Forwarded-For to pass the originating client address. If a proxy is configured to set this header, it can leak your real IP just as effectively as the others.
Why Cheap Proxies Leave These Headers Intact
Properly configured elite proxies strip all forwarding headers before passing requests to the destination. They replace or remove X-Forwarded-For, suppress the Via header, and present themselves as a clean origin rather than an intermediary. Doing this requires intentional configuration. It does not happen by default with every proxy setup.
Free proxies and poorly maintained paid ones often skip this step. Some run on default configurations that were never hardened. Others are just relay services where the operator never considered header hygiene. The result is a proxy that masks your IP at the network level but broadcasts your original address at the application level. A website receiving those requests sees both the proxy IP in the connection and your real IP in the header.
There is also a category called transparent proxies that do not even attempt to hide the fact that you are using an intermediary. These are sometimes used on corporate or ISP networks for caching purposes. If you end up routing through one unknowingly, the headers it adds can expose your traffic in ways you did not anticipate.
Running the Diagnostic: What a Remote Server Actually Sees
The most reliable way to check your headers is to use a tool that reflects back exactly what your browser sent. This is not a test you run on your local machine. You need to see what the server received, which means making a real request and reading the result from the other side.
Here is the step-by-step process to run the check properly:
- Enable your proxy as you normally would, through your browser settings, system settings, or whatever client you use.
- Open a header inspection tool in your browser. A straightforward way to do this is to check HTTP headers using a live reflection tool that shows you exactly what your connection is sending to a remote server.
- Look specifically for X-Forwarded-For, Via, and X-Real-IP in the output. Write down the exact values shown.
- Compare those values to your real IP address. Find your real IP by temporarily disabling the proxy and visiting any plain IP lookup page.
- Check whether the Via header contains any proxy identifiers, version strings, or hostnames that could identify the intermediary handling your traffic.
If your real IP appears anywhere in the X-Forwarded-For chain or in X-Real-IP, your proxy is leaking. If Via is present and shows proxy fingerprints, the destination server knows you are not connecting directly, even if it cannot pin down your exact address.
What the Headers Reveal About Proxy Quality
Not all proxies handle these headers the same way. The differences between proxy types are significant for anyone who needs genuine privacy rather than a cosmetic IP change.
Elite, Anonymous, and Transparent Proxy Header Behavior
| Proxy Type | X-Forwarded-For | Via Header | Real IP Exposed? |
|---|---|---|---|
| Elite (High Anonymity) | Not present | Not present | No |
| Anonymous | Not present | Present (proxy use visible) | No, but proxy is detectable |
| Transparent | Contains real IP | Present | Yes |
| Misconfigured Paid Proxy | May contain real IP | Often present | Depends on configuration |
What Clean Header Output Actually Looks Like
When a proxy is configured correctly for privacy, the header output from an inspection tool should be minimal. Your request should arrive at the destination looking like it came from a standard browser with no signs of an intermediary in the chain. That means no X-Forwarded-For field, no Via header, and no X-Real-IP. The headers present should be the normal browser headers: Accept, Accept-Language, User-Agent, and similar fields that are part of ordinary HTTP communication.
The User-Agent header deserves a mention here because it is often overlooked during this kind of check. Your browser sends a string identifying itself, including version and operating system details. A proxy does not strip this by default. If your User-Agent is unusual or very specific, it can act as a fingerprint on its own. That is a separate issue from forwarded headers, but it is worth noting when you are assessing your overall exposure from a single connection.
A truly clean result from a header inspection tool shows the proxy IP as the only visible network source and contains no fields that reference the original connection. If you see that output, your proxy is doing its job at the application layer, not just the network layer.
Fixing the Leak When Headers Are Not Clean
If your diagnostic shows leaked headers, the fix depends on what kind of proxy setup you are running. For users managing their own proxy server, the solution involves updating the configuration to suppress forwarding headers. In Squid, you set the forwarded_for directive to “off” and use the request_header_access rules to block outgoing Via headers. In NGINX acting as a forward proxy, you explicitly clear X-Forwarded-For and Via in the relevant configuration block so they are never passed upstream.
For users relying on a third-party proxy service, the path forward is different. Contact the provider directly and ask about their header-stripping policy. A reputable provider should be able to confirm whether their nodes are configured as elite or anonymous and should explain what headers they modify on outgoing requests. If the provider cannot give a clear answer to that question, or if they do not offer elite-level proxies at all, that tells you something important about how much they have invested in proper configuration.
Switching services is sometimes the correct decision. Not all proxy providers are equal in how they treat request metadata. If your current proxy is leaking your real IP through headers, no amount of IP verification is going to fix the underlying problem because the issue is not with the IP layer at all.
The Gap Between What Your Proxy Shows and What It Actually Hides
An IP address change is visible and easy to confirm. Header leaks are quieter, and that is exactly what makes them more dangerous in practice. You can spend months believing you are protected while every request you send announces your real IP to any server that looks past the surface connection.
Running a header inspection takes a few minutes. It requires no special software and no technical background beyond reading a short list of values. If the test comes back clean, you have real evidence that your proxy is doing more than just swapping the visible address. If it does not, you know precisely where to focus next.
Privacy is not just about the IP address a site logs from the connection. It is about every piece of data that travels with the request, including the fields that most users never think to inspect. Headers are a small detail, but they are the detail that misconfigured proxies consistently get wrong. Checking them once is a smarter investment than assuming everything is fine because the surface reading looks correct.